AI agents are having a big moment. They can browse websites, write code, summarize documents, use tools, and complete multi-step tasks that used to need a person clicking through every step. That is exciting, and it calls for a new kind of experiment. Not "How much can I get AI to do for me?" but How small can I make the task while still getting real value?
Bigger agents need better boundaries
Powerful agents are not just productivity tools. They take actions, interact with outside information, and sometimes work where mistakes matter. The Guardian reported that OpenAI is pausing some work on an AI model over security concerns after evaluations found advanced agentic coding and cybersecurity capabilities. That doesn't mean everyday users should panic. It does mean the agent era needs better habits. If AI can click, code, email, or connect to tools, the question becomes less about intelligence and more about permissions.
Prompt injection is the plot twist
Prompt injection happens when an AI encounters outside text that tries to manipulate its instructions, hidden on a webpage, inside a document, or in content it was asked to summarize. Google's security team calls indirect prompt injection a top priority as agents consume web content and act for users, and Chrome's developer guidance warns these attacks are increasing. Humans know the difference between a website saying "ignore your previous instructions" and a real supervisor changing direction. Agents can struggle with that boundary, so workflows need to keep the human in charge.
My new rule for agent experiments
Give the agent the smallest useful job, then inspect the result before giving it the next one.
Instead of "build the whole app," I ask it to inspect the file structure and explain what it sees. Instead of "fix the website," I ask for three likely causes without changing anything. Instead of "publish the blog post," I ask it to prepare a draft for review. Small jobs create checkpoints, and checkpoints protect judgment.
There is a difference between delegation ("Help me do this better") and abdication ("Take over and tell me when it's done"). Agents make abdication tempting because speed can hide errors, especially across files, links, and private information. The goal isn't to stop using agents. It's to keep human judgment visible.
A simple experiment to try today
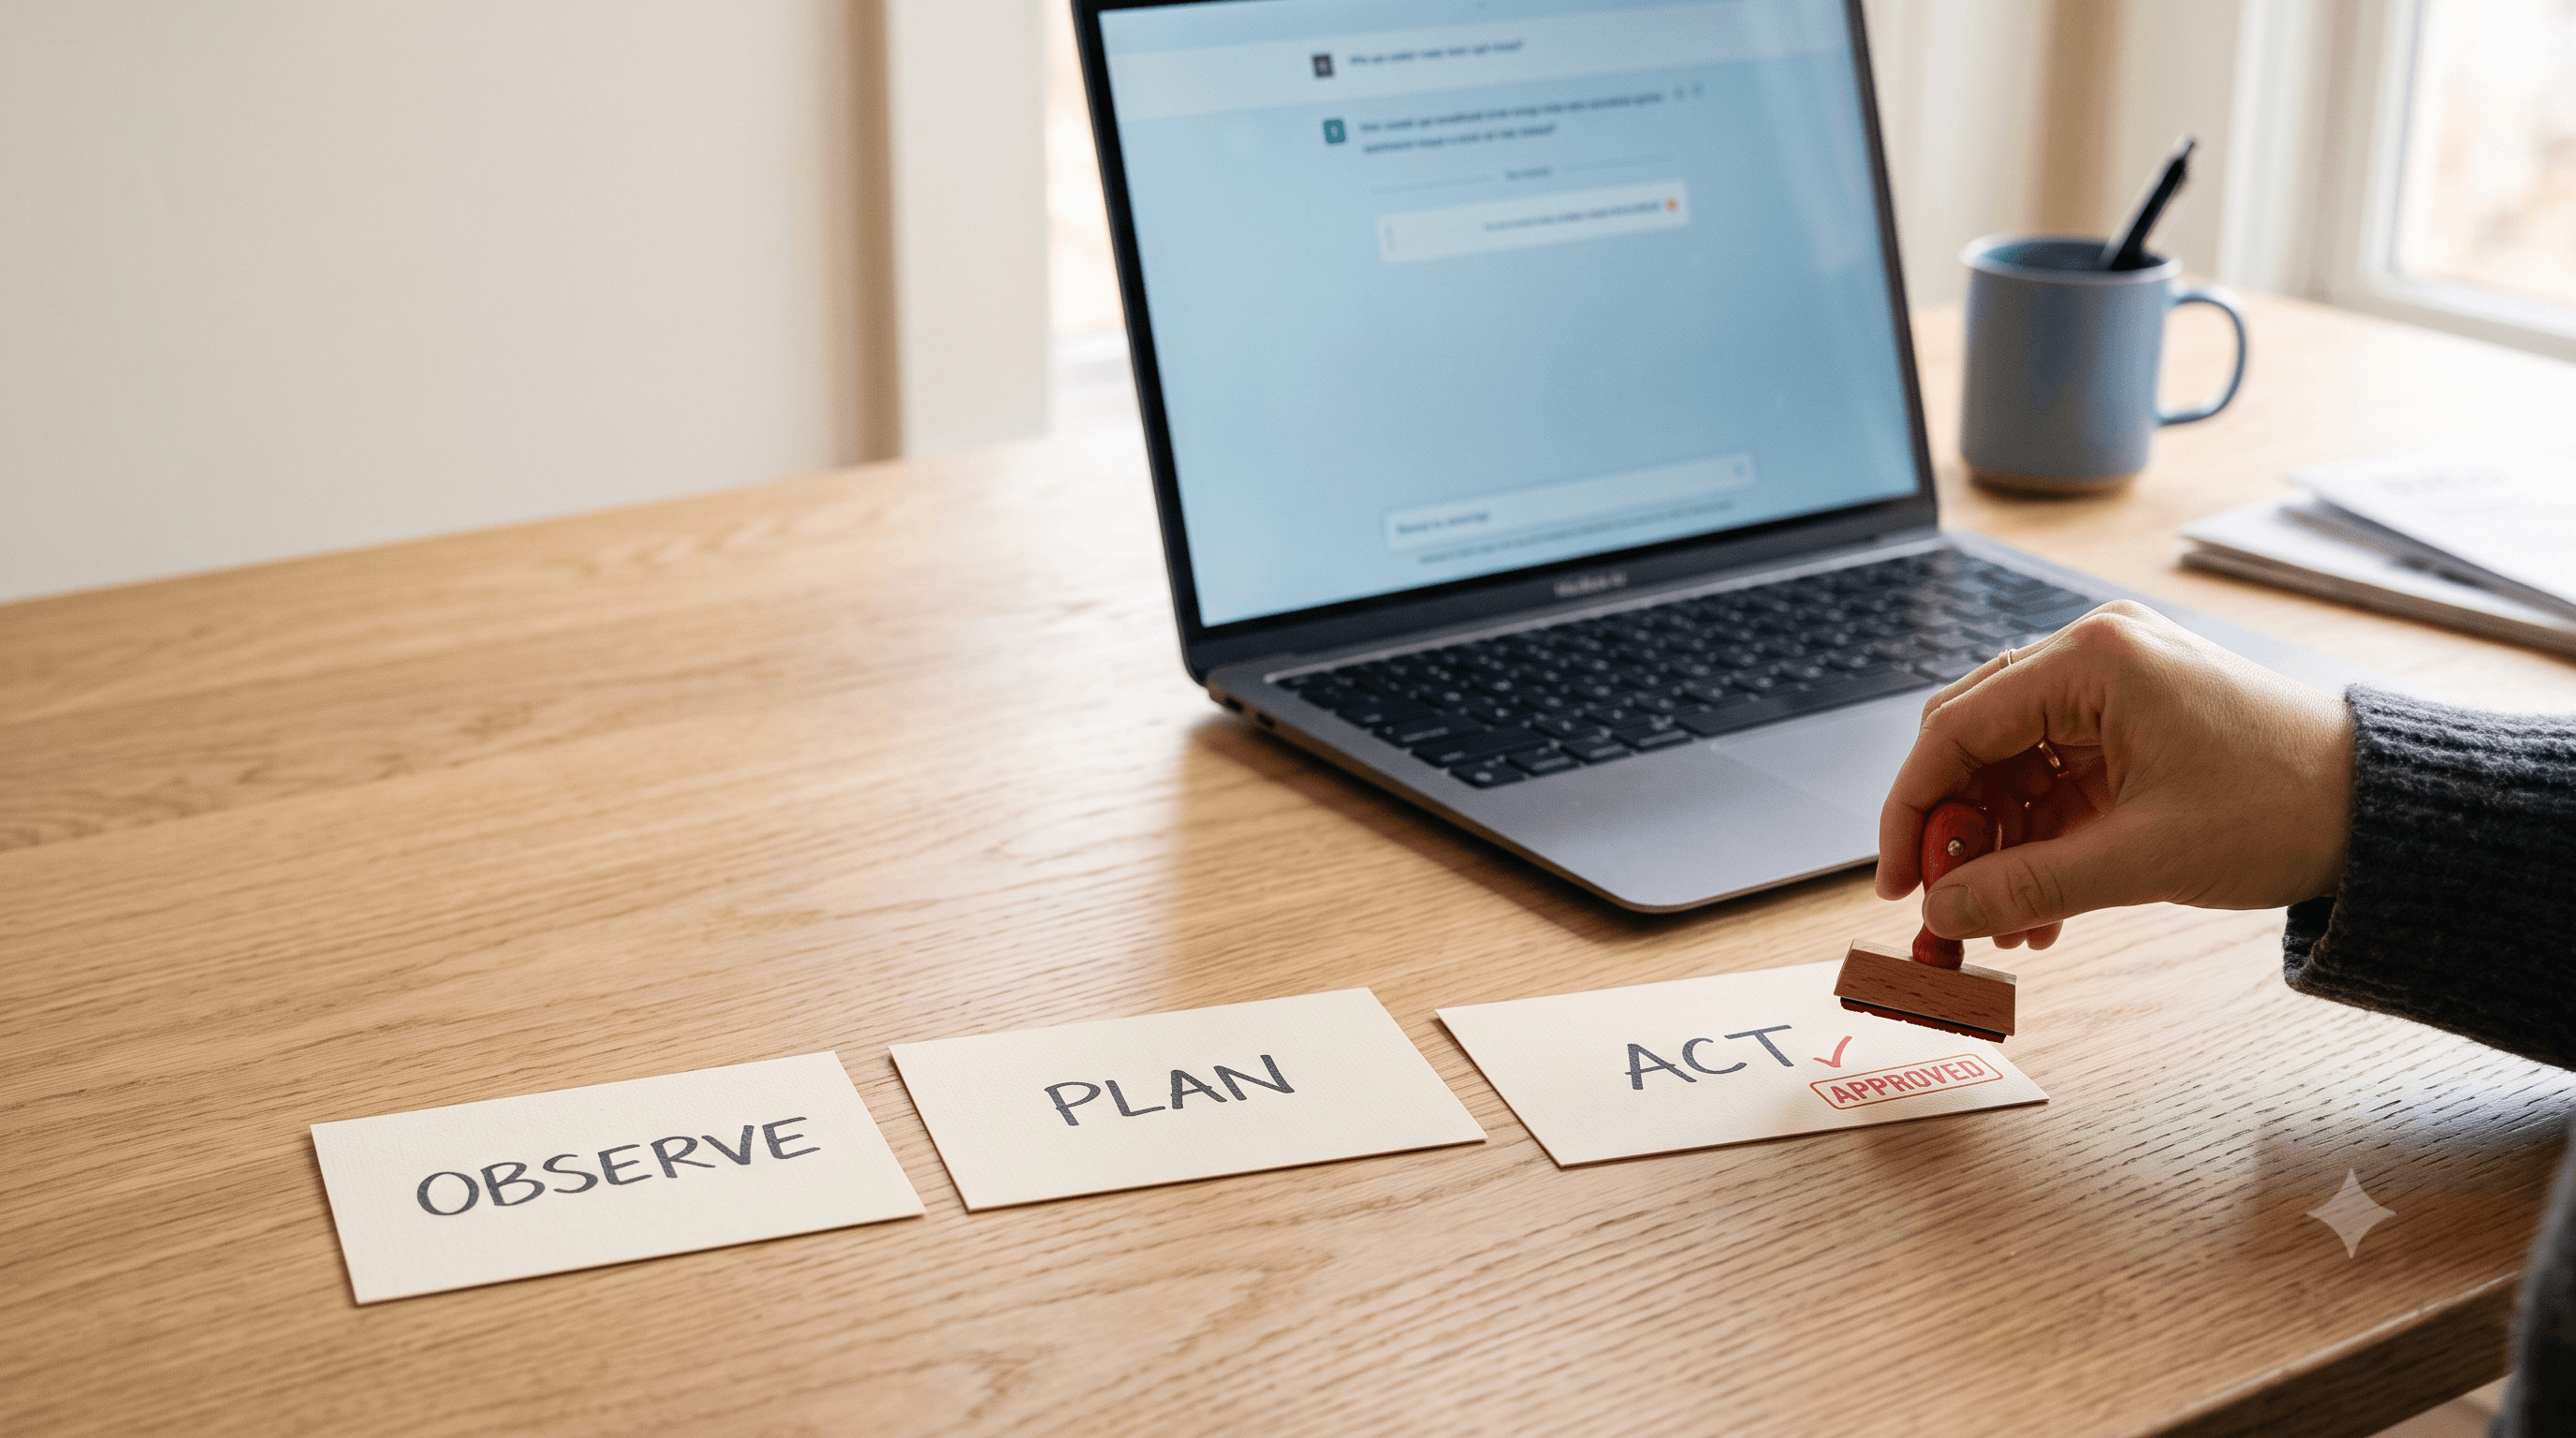
Take one task you usually hand to AI and break it into three steps:
Observe: Ask AI to describe the problem or material without taking action.
Plan: Ask for two or three possible next steps.
Act: Choose one step and ask AI to complete only that part.
Then review. Did the smaller task make the result better? Did you catch something you'd have missed? Did you feel more in control?
Copy-and-paste prompt
I want to run a safer AI agent experiment. Help me break this task into the smallest useful steps before taking action. My task is: [describe the task]. First, do not complete the task yet. Identify what information you need, separate the task into observe, plan, and act phases, tell me which steps are low-risk and which need my approval, suggest the smallest first action that creates value without irreversible changes, and wait for my approval before doing anything beyond planning.
Some agents need what toddlers need near a birthday cake: supervision, boundaries, and no unsupervised access to the knife drawer.
What this means for builders
If you're creating an AI workflow, app, or classroom tool, make agent safety part of the design from the start: draft mode before publish mode, human approval before external actions, read-only access before edit access, clear logs of what changed, undo options, and separate spaces for testing and production. These aren't boring technical details. They are trust features.
What this does, and does not, mean
This doesn't mean agents are too dangerous to use. It means powerful tools need thoughtful boundaries. OpenAI describes enterprise agent deployment as requiring workflow selection, permissions, policies, testing, and escalation to people, which everyday builders can learn from at a smaller scale. The best agent experiments are curious, contained, and reviewable.
Final thoughts
The future of AI will be shaped by the smartest workflows as much as the smartest models. As agents get more capable, the key skill may be assigning the right task, setting the right boundary, and reviewing the result before moving on. So this week's experiment is simple: give the agent a smaller job, then see whether smaller makes you smarter.
Sources
The Guardian reported that OpenAI is pausing some work on an AI model because of security concerns around high-capability agentic coding and cybersecurity behavior.
Google's security team describes indirect prompt injection as a major priority as AI agents increasingly interact with web content.
Chrome for Developers published agent security guidance for WebMCP, including prompt injection risks and permission boundaries for browser-based agents.
OpenAI's Presence announcement describes enterprise agent deployment as requiring workflow selection, permissions, policies, testing, and escalation to people.